Capability

A security command centre, built in

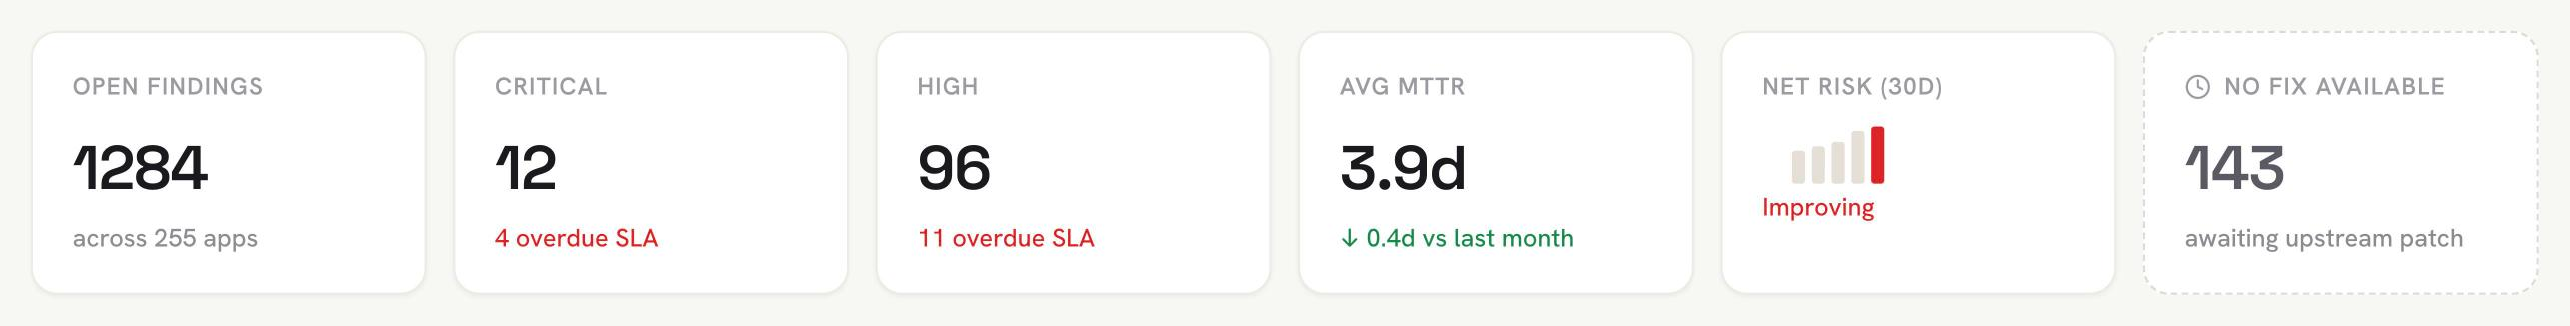
Substrait gives your security team one console for every finding across every tool. It opens on one page that answers how exposed you are right now, using your own severity names.

Last updated

What the console shows

  • Every finding across every tool, in one list
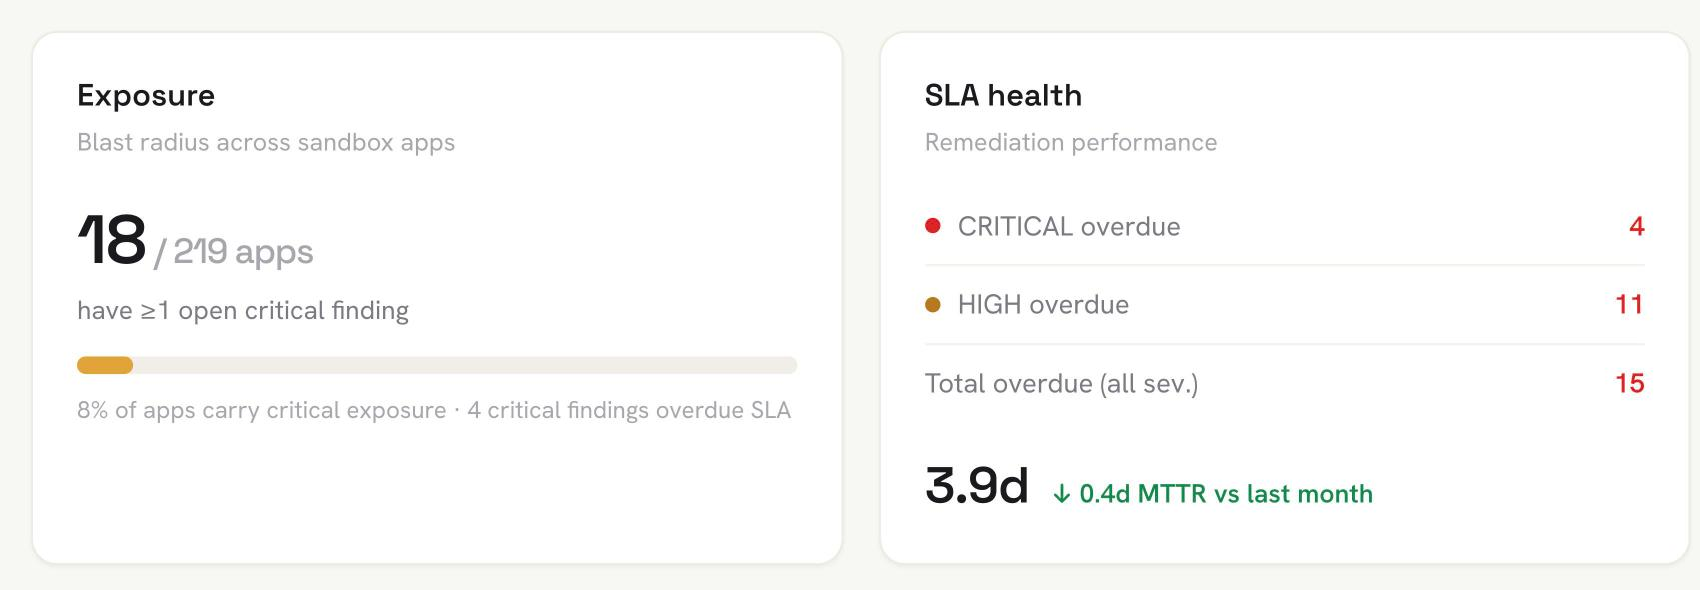
  • How exposed the organisation is now: open findings, findings past their deadline by tier, time to fix, a trend, and the tools with the most risk
  • Response deadlines for each tier, and an activity log
  • One environment at a time, never dev and production blended
  • “No fix available” as its own status, so a finding nobody can fix yet does not inflate the headline risk

Your words, not ours

The console uses your organisation’s own severity names. If your team says P0, so does Substrait.

Substrait security command centre: open findings, critical and high findings with overdue counts, average time to fix, net risk trend and findings with no fix available.
The first view of the security command centre. Product UI. Sample data.
Substrait security command centre: findings past their response deadline, by tier.
Findings against their response deadlines. Product UI. Sample data.

Related

Start with a result, not a rollout.

Book a demo and bring one real use case. We will show you how a tool your people build goes live on Substrait, with its data approved and its security check passed.